Technology and Science03 April, 20261 min read
TeamPCP Hacks European Commission via Poisoned Trivy, Steals 340GB Data
This article is an automated aggregation of coverage from news outlets. Our editorials offer in-depth analysis curated by the NewsCord team.
CERT-EU attributes breach to TeamPCP; supply-chain attack via poisoned Trivy updates. Affected entities: 29–30 EU bodies; AWS cloud compromised in the breach.
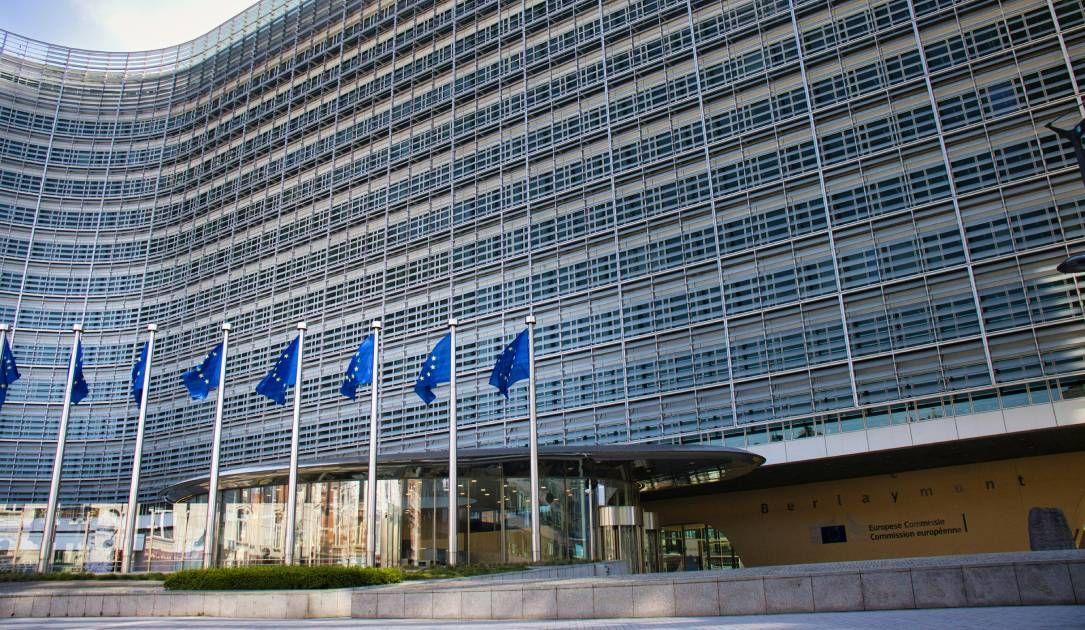
Supply Chain Attack Breaches EU Cloud
The European Commission suffered a massive data breach after TeamPCP exploited a poisoned version of Trivy to steal AWS API keys. The breach was first detected on March 24 but originated on March 19.
Approximately 340 gigabytes of data were exfiltrated, affecting 71 clients of the Europa web hosting service. The commission's Cybersecurity Operations Center failed to detect the intrusion for five days.
ShinyHunters Leak Stolen Data
The extortion group ShinyHunters published the stolen dataset on their leak site. This dual attribution is unusual and complicates response efforts.
At least 52,000 files containing sent email messages were included. The leak contained personal data including names and email addresses.
Investigation Reveals Attack Techniques
CERT-EU's investigation revealed multiple advanced techniques used by the attackers. The breach originated from a supply chain compromise of Trivy that was inadvertently downloaded by the Commission.
The attackers used TruffleHog to scan for additional secrets and created new access keys to evade detection. This cascading failure underscores the complexities of securing modern digital environments.