Crypto18 August, 20262 min read
BitBox Releases Firmware Update for Two Severe Hardware Wallet Vulnerabilities, Including Memory Corruption
This article is an automated aggregation of coverage from news outlets. Our editorials offer in-depth analysis curated by the NewsCord team.
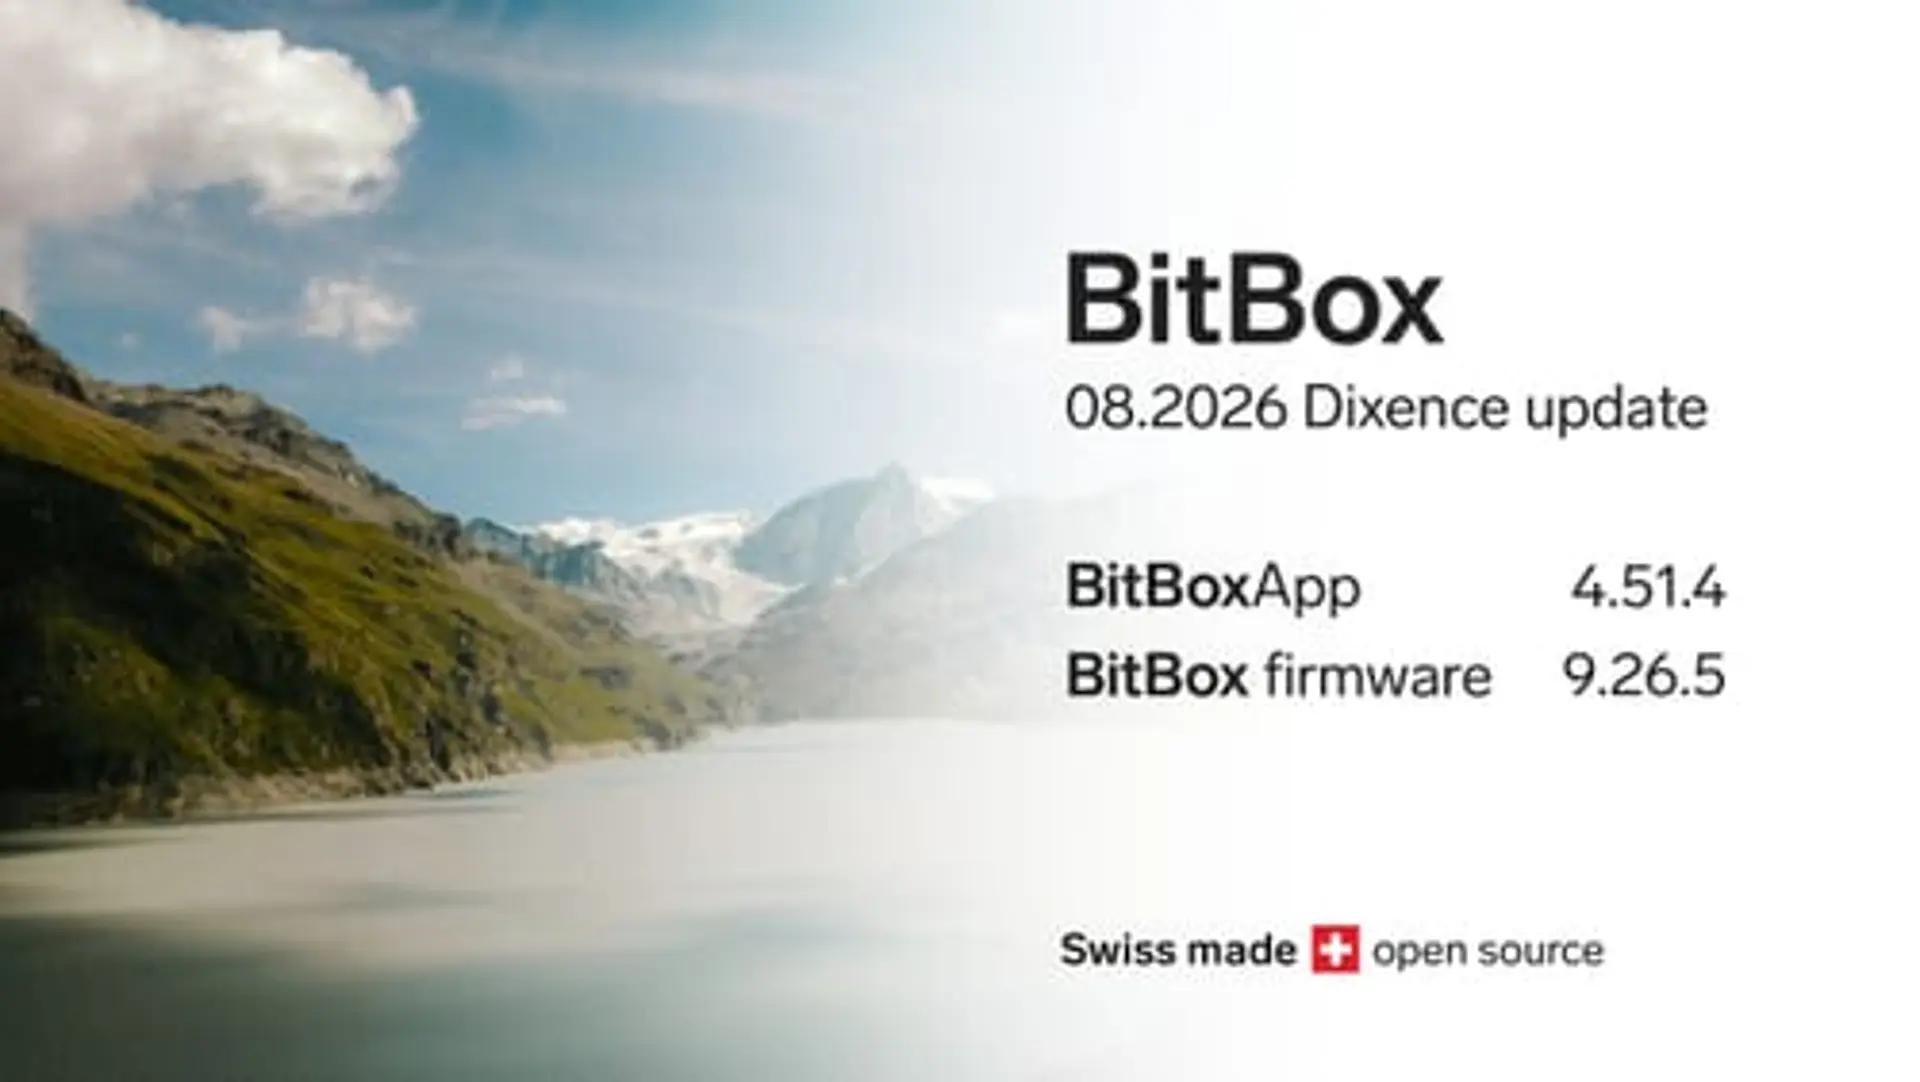
BitBox released Dixence update (firmware 9.26.5) addressing two severe vulnerabilities in BitBox02 devices One flaw allowed malicious firmware installation; memory corruption in Multi editions; both fixed
BitBox issues urgent firmware fix
BitBox, the Swiss maker of self-custody hardware wallets, released a firmware update to address two security issues it described as “severe,” saying the fixes reduce the risk of malicious firmware installation and prevent scenarios involving its Silent Payments feature that could cause Bitcoin to be locked to an unintended address. BitBox said it has not received any information indicating either vulnerability has been exploited in the wild or that users have lost funds as a result, and it urged users to update their BitBoxApp and device firmware to the latest version, 9.26.5.
The first vulnerability involves memory corruption affecting “Multi editions of BitBox02 and BitBox02 Nova” when those devices have not been configured with a wallet, and BitBox said a malicious host could exploit the bug to execute arbitrary code and potentially install malicious firmware. The second issue relates to BitBox’s Silent Payments implementation, where BitBox said a malicious host could lock Bitcoin to an unintended address, and while it said the flaw does not enable direct theft, it argued an attacker could demand a ransom in exchange for cooperation in recovering the coins.
How the attacks could work
BitBox said the memory-corruption flaw could be exploited by a malicious host connected to an affected wallet before the device had been configured with a wallet, enabling arbitrary code execution and potentially allowing the host to install malicious firmware. Cryptonews.net reported that BitBox said direct theft was not possible through the Silent Payments vulnerability, but that an attacker could potentially demand a ransom to cooperate in recovering the coins.
In the Silent Payments scenario, BitBox said a malicious host could lock Bitcoin to an unintended address, leaving the victim unable to recover the Bitcoin without cooperation and potentially forcing a ransom exchange. The patch also arrives after Coldcard’s earlier issues, with Cointelegraph citing Galaxy Research figures that Coldcard-related losses exceeded $112 million and that about 1,778.6 BTC were swept from more than 8,600 addresses.
Broader wallet ecosystem risk
Beyond device firmware, the sources describe how hardware-wallet security can be shaped by surrounding services, including data breaches that exposed customer and order information for more than 53,000 customers involving Trezor and SafePal. Cointelegraph reported that Trezor attributed exposure of 13,689 customers’ data to shipping provider ShipMonk, while SafePal said an authorization flaw in an order-tracking plug-in exposed details tied to 39,798 customers.
Both companies warned that the information could be used for targeted phishing and impersonation attempts, and Cointelegraph framed the BitBox update as part of a broader pattern of incidents affecting hardware-wallet ecosystems. In a separate report, Cryptonews.net said BitBox released the update after Coldcard thefts and underscored that weaknesses in devices designed to protect private keys can become points of failure, even when BitBox said it had received no reports of exploitation or user fund loss tied to its two vulnerabilities.