Technology and Science16 September, 20263 min read
Google Patches Pixel Modem Zero-Day CVE-2026-58704 Exploited in Targeted Attacks
This article is an automated aggregation of coverage from news outlets. Our editorials offer in-depth analysis curated by the NewsCord team.
CVE-2026-58704 in Pixel modem is being weaponized in limited, targeted attacks. Google released September 2026 patches addressing 110 Pixel vulnerabilities, including a zero-day.

Pixel modem zero-day patched
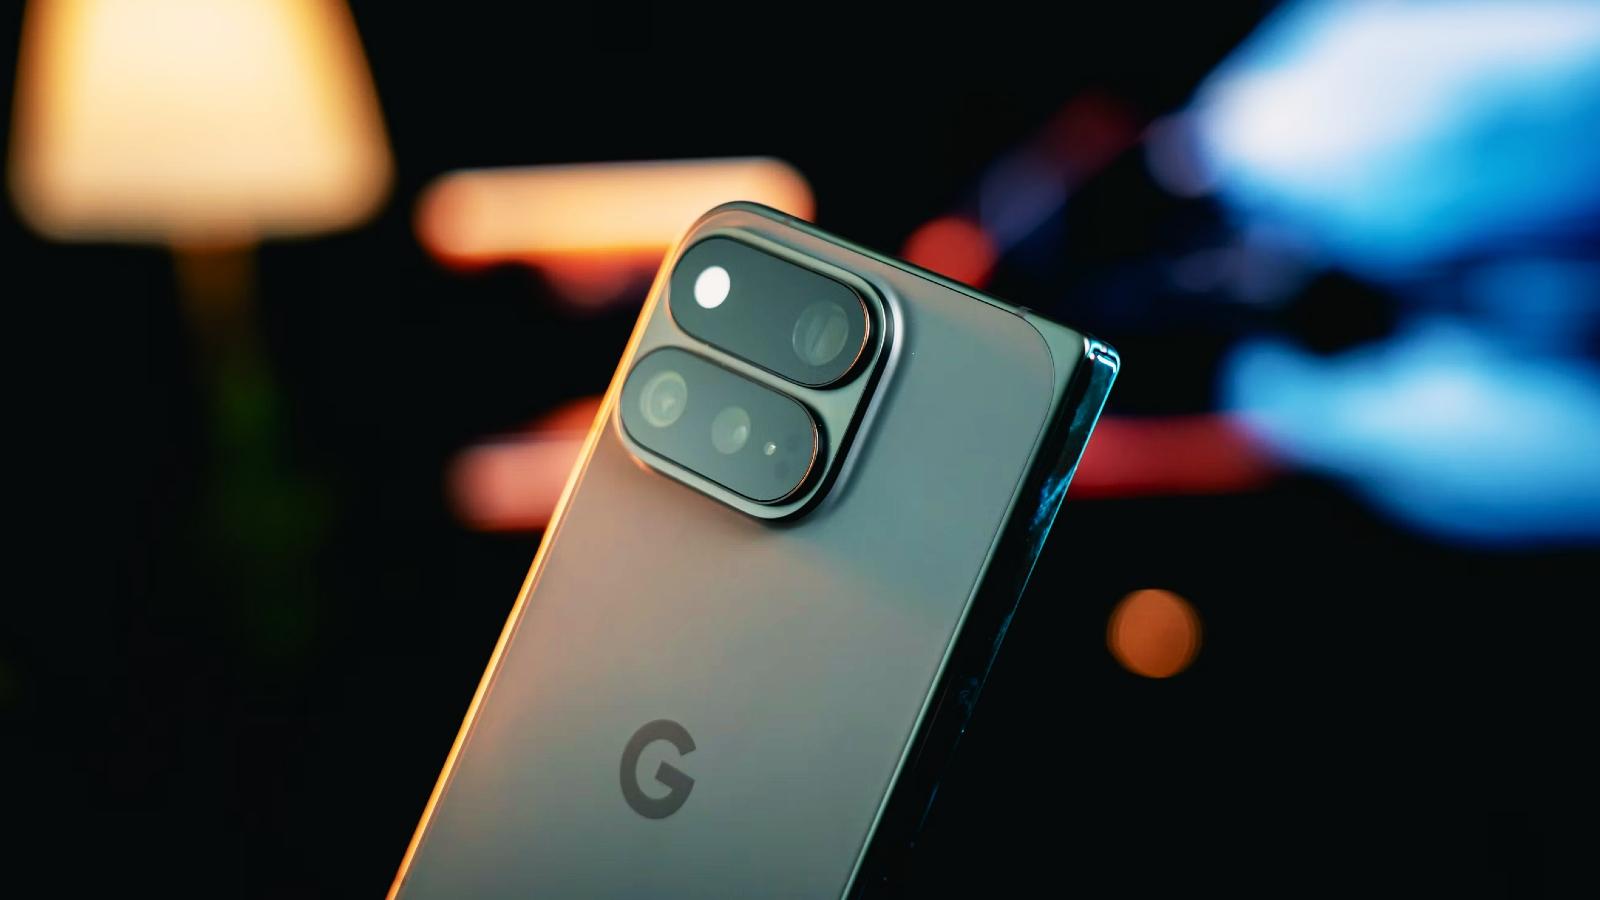
Google patched a Pixel modem zero-day, tracked as CVE-2026-58704, that it said was being exploited in “limited, targeted exploitation” in attacks against Pixel devices. The vulnerability is described in Google’s advisory as “a possible permission bypass due to a logic error in the code,” which “could lead to remote (proximal/adjacent) escalation of privilege with no additional execution privileges needed.” Google said the flaw does not require user interaction, and it urged Pixel users to update to the 2026-09-05 security patch level or later to be protected against the issues covered by the Pixel bulletin.
“There are indications that CVE-2026-58704 may be under limited, targeted exploitation.”
Cybernews reported that Google’s Pixel Update Bulletin warned the high-severity bug could let an attacker take control of a targeted device and “does not require the victim to click a link, download an app, or open a malicious file.” The September 2026 Pixel security update that includes the emergency patch addresses 110 vulnerabilities, with Cybernews stating it “fixes 12 bugs that could let attackers run malicious code remotely and 89 that could give them higher-level access.”
How the attacks work
Google’s advisory ties CVE-2026-58704 to the Modem subcomponent, describing “a possible permission bypass due to a logic error in the code” that can enable privilege escalation from an adjacent or proximal position. TechCrunch characterized the bug as being exploited in limited and targeted cyberattacks, saying Google reported the bug “has now been patched” after it was found in Pixel phones’ modem. Cybersecurity coverage emphasized that the exploit can be “zero-click,” with TechCrunch stating the bug “can be exploited silently and without any interaction from the phone owner.”
BleepingComputer echoed Google’s warning that “All supported Google devices will receive an update to the 2026-09-05 patch level,” and it described the flaw as stemming from improper authorization and protection mechanism failure weaknesses. BleepingComputer also quoted the advisory’s mechanism, stating “This could lead to remote (proximal/adjacent) escalation of privilege with no additional execution privileges needed,” while noting the update tags 109 other issues including “12 remote code execution and 89 privilege escalation vulnerabilities rated critical or high severity.”
What’s at stake next
Google’s guidance centers on urgency for Pixel owners, with BleepingComputer directing users to go to Settings > Security & privacy > System & updates > Security update, tap Install, and restart their devices to complete the update process. The same coverage tied the risk to the modem layer, explaining that successful exploitation can allow attackers with access to an adjacent network and basic privileges to “escalate privileges in low-complexity attacks that don't require user interaction.” TechCrunch reported that Google did not say who was exploiting the bug, and it noted that a spokesperson “did not return a request for comment.”
In parallel, Security Affairs framed the modem flaw as particularly notable because it “does not require user interaction,” while also stating that Google “has not disclosed who exploited the vulnerability, how many devices were targeted, or what the attacks were designed to achieve.” For defenders and users, the practical consequence in the sources is that the 2026-09-05 patch level is the line for remediation, since Google said devices using the 2026-09-05 security patch level or later are protected against the issues covered by the Pixel bulletin and the September Android Security Bulletin.