Technology and Science14 September, 20262 min read
Hackers Hijack Verified r/hbomax Reddit Account to Push ClickFix Malware Ads
This article is an automated aggregation of coverage from news outlets. Our editorials offer in-depth analysis curated by the NewsCord team.
Hackers hijacked HBO Max's Reddit account to publish 108 ClickFix ads. Ads targeted Windows and macOS users, enabling information-stealing malware.

ClickFix via HBO Max
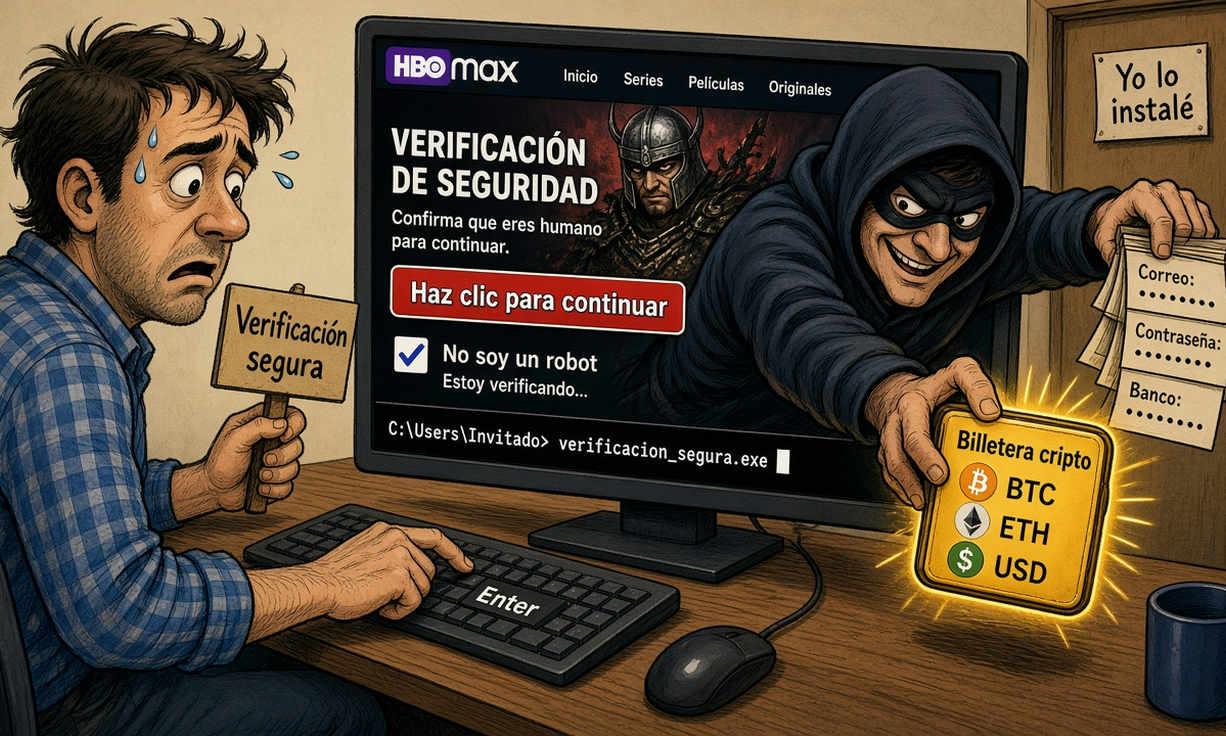
Hackers hijacked the verified u/hbomax Reddit account and used it to launch 108 malicious advertisements over approximately 48 hours, according to analysis by security firms Hudson Rock and ADAMnetworks. The ads pushed victims to pages that looked like HBO Max but instructed them to copy and paste a command into Windows Command Prompt or macOS Terminal, turning users into “an unwitting participant in the infection.”
One of the fake HBO Max sites used in the campaign was hbomaxx[.]us, and clicking the download button did not download an app but instead displayed instructions telling visitors to open Terminal and paste a command. Security researchers said the ClickFix technique relies on social engineering rather than automatically exploiting a vulnerability, and that the command execution can steal passwords, account credentials, active authentication sessions, and information from cryptocurrency wallets.
What researchers saw
Hudson Rock and ADAMnetworks said the campaign was initially discovered after a Reddit user spotted an advertisement posted from the verified HBO Max account promoting what appeared to be a native HBO Max application for macOS. BleepingComputer quoted the Reddit user warning that the advert takes you to hbomaxx[.]us and that clicking “these opens up the classic infostealer/clickfix paste this command to download.”
BleepingComputer also reported that one of the macOS commands it saw used Base64 encoding, and after decoding it contained the command beginning with “export _watch_v2=97d9d8dc;curl -sL”. Researchers linked the HBO Max ads to a larger operation they call PasteSwitch, which they said targets both Windows and macOS systems and has been used to distribute information stealers, loaders, cryptocurrency clippers, and fake cryptocurrency wallet applications.
Defenses and uncertainty
Reddit confirmed it had detected the compromise of the HBO Max account, and after the incident was discovered the account was blocked and the ads were removed, while the exact number of people who clicked the dangerous ads remains unknown. TechCrunch reported that Reddit told it “it recently learned that an HBO Max account authorized to run advertisements on Reddit was compromised and used to run ads containing malicious links,” and that Reddit locked the account and removed the ads.
TechCrunch also said companies that run fleets of Windows computers can block access to Command Prompt or PowerShell across an entire domain to prevent them from being exploited, citing security researcher Kevin Beaumont. The reporting also noted that it is unclear how many people clicked the fake ads or how many were ultimately compromised, and that Warner Brothers Discovery, which owns HBO, did not respond to a request for comment.