Technology and Science19 August, 20262 min read
Hackers Steal Medical Records From CareCloud, Affecting More Than 3.75 Million People
This article is an automated aggregation of coverage from news outlets. Our editorials offer in-depth analysis curated by the NewsCord team.
Hackers stole personal information and medical records of more than 3.75 million people from CareCloud. Breach began in March; attackers had six days of access to cloud data.

CareCloud breach confirmed
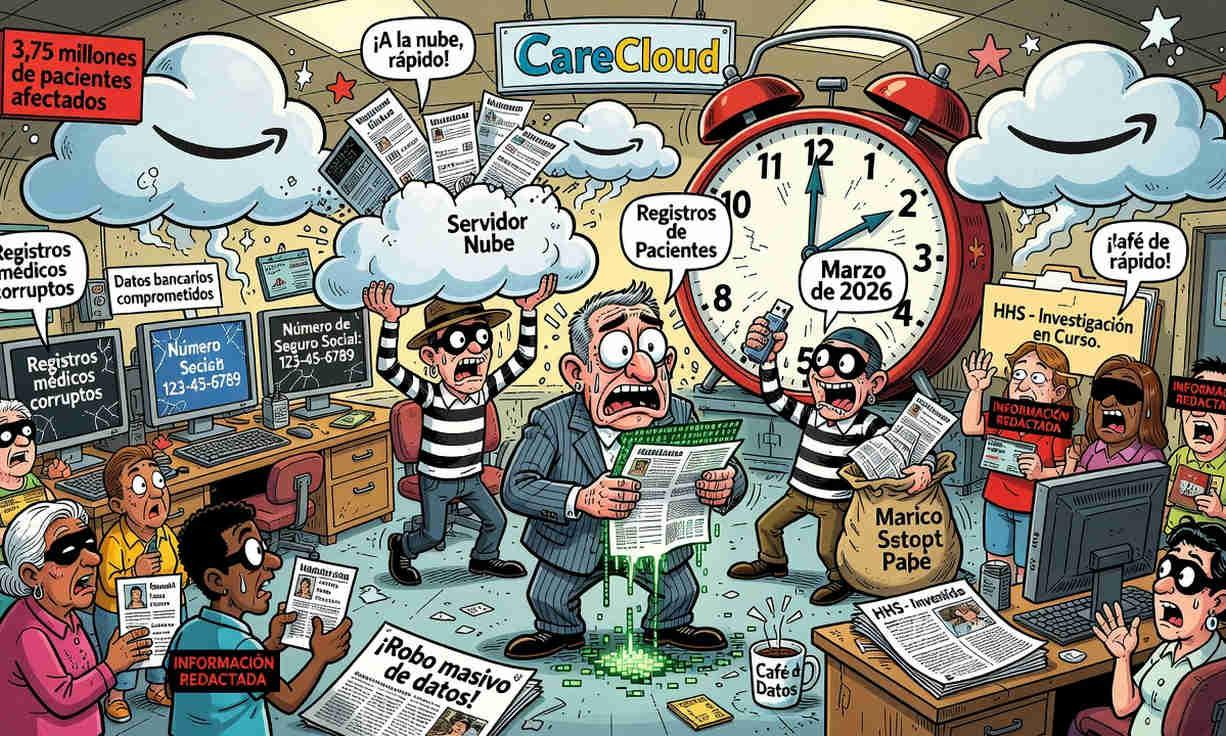
CareCloud confirmed to U.S. federal regulators that hackers stole personal information and medical records of more than 3.75 million people in a March cyberattack, revising the breach’s scale upward to rank as the fifth-largest health data theft of 2026 so far. The company said the unauthorized access lasted six days in one of its cloud environments, with the breach disclosed in March and later confirmed in July as involving data stolen from its Amazon Web Services environment.
CareCloud is based in New Jersey and provides electronic health record storage to tens of thousands of healthcare providers around the United States, meaning the breach affects people far beyond those directly using its service. TechCrunch reported that CareCloud detailed the March data breach in a filing with the Department of Health and Human Services (HHS) on Monday, and that the number of affected victims was revised up in an update on Tuesday.
What was stolen
CareCloud’s filings and disclosures described stolen information that includes names, postal addresses, Social security numbers, medical records, government IDs such as passports and driver's licences, and banking information. The News International wrote that CareCloud confirmed in July that the hackers had stolen the data from its Amazon Web Services environment, after the company said in March that unauthorized individuals had accessed patient data in one of its cloud environments for six days.
TechCrunch said the stolen data includes patients’ names, postal addresses, Social Security numbers, and their medical and health information, along with government-issued identification numbers such as passports and driver’s licenses, and banking and financial information. Both outlets also reported that CareCloud chief executive Stephen Snyder did not respond to multiple requests for information about the incident, including whether the company has paid the hackers and who is responsible for cybersecurity.
Wider healthcare breach context
The CareCloud breach is occurring alongside other healthcare cyber incidents in 2026, including TriZetto’s March confirmation that a 2024 breach compromised the personal information of 3.4 million patients. TechCrunch said dental insurance giant DentaQuest has had the largest data breach this year so far, with at least 15 million people’s personal and health information being affected, according to HHS’ running tally of healthcare data breaches.
The News International reported that Craneware revealed another breach in July but did not reveal how many patients had their data compromised, while also noting that CareCloud has not addressed the breach publicly since its March revelation. In the same period, CareCloud told regulators that the breach began in March and that hackers exfiltrated data from an Amazon Web Services account, leaving the company’s next steps and accountability questions unresolved as Snyder declined to respond.