Cryptoupdated 57m ago3 min read
Ledger Says LTE Spy Chip Stole Recovery Phrases From CryptoBilis Wallets
This article is an automated aggregation of coverage from news outlets. Our editorials offer in-depth analysis curated by the NewsCord team.
LTE-enabled hardware implants in CryptoBilis wallets captured recovery phrases and transmitted them via cellular networks. Ledger reports losses up to $93.2 million across over 300 wallets tied to the incident.
11 outlets told this the same way.
Spy chip mechanism
Ledger said a covert component inside some Ledger devices sold by CryptoBilis transmitted wallet keys by capturing users’ recovery phrases from the device screen and sending them to attackers over an LTE mobile network.
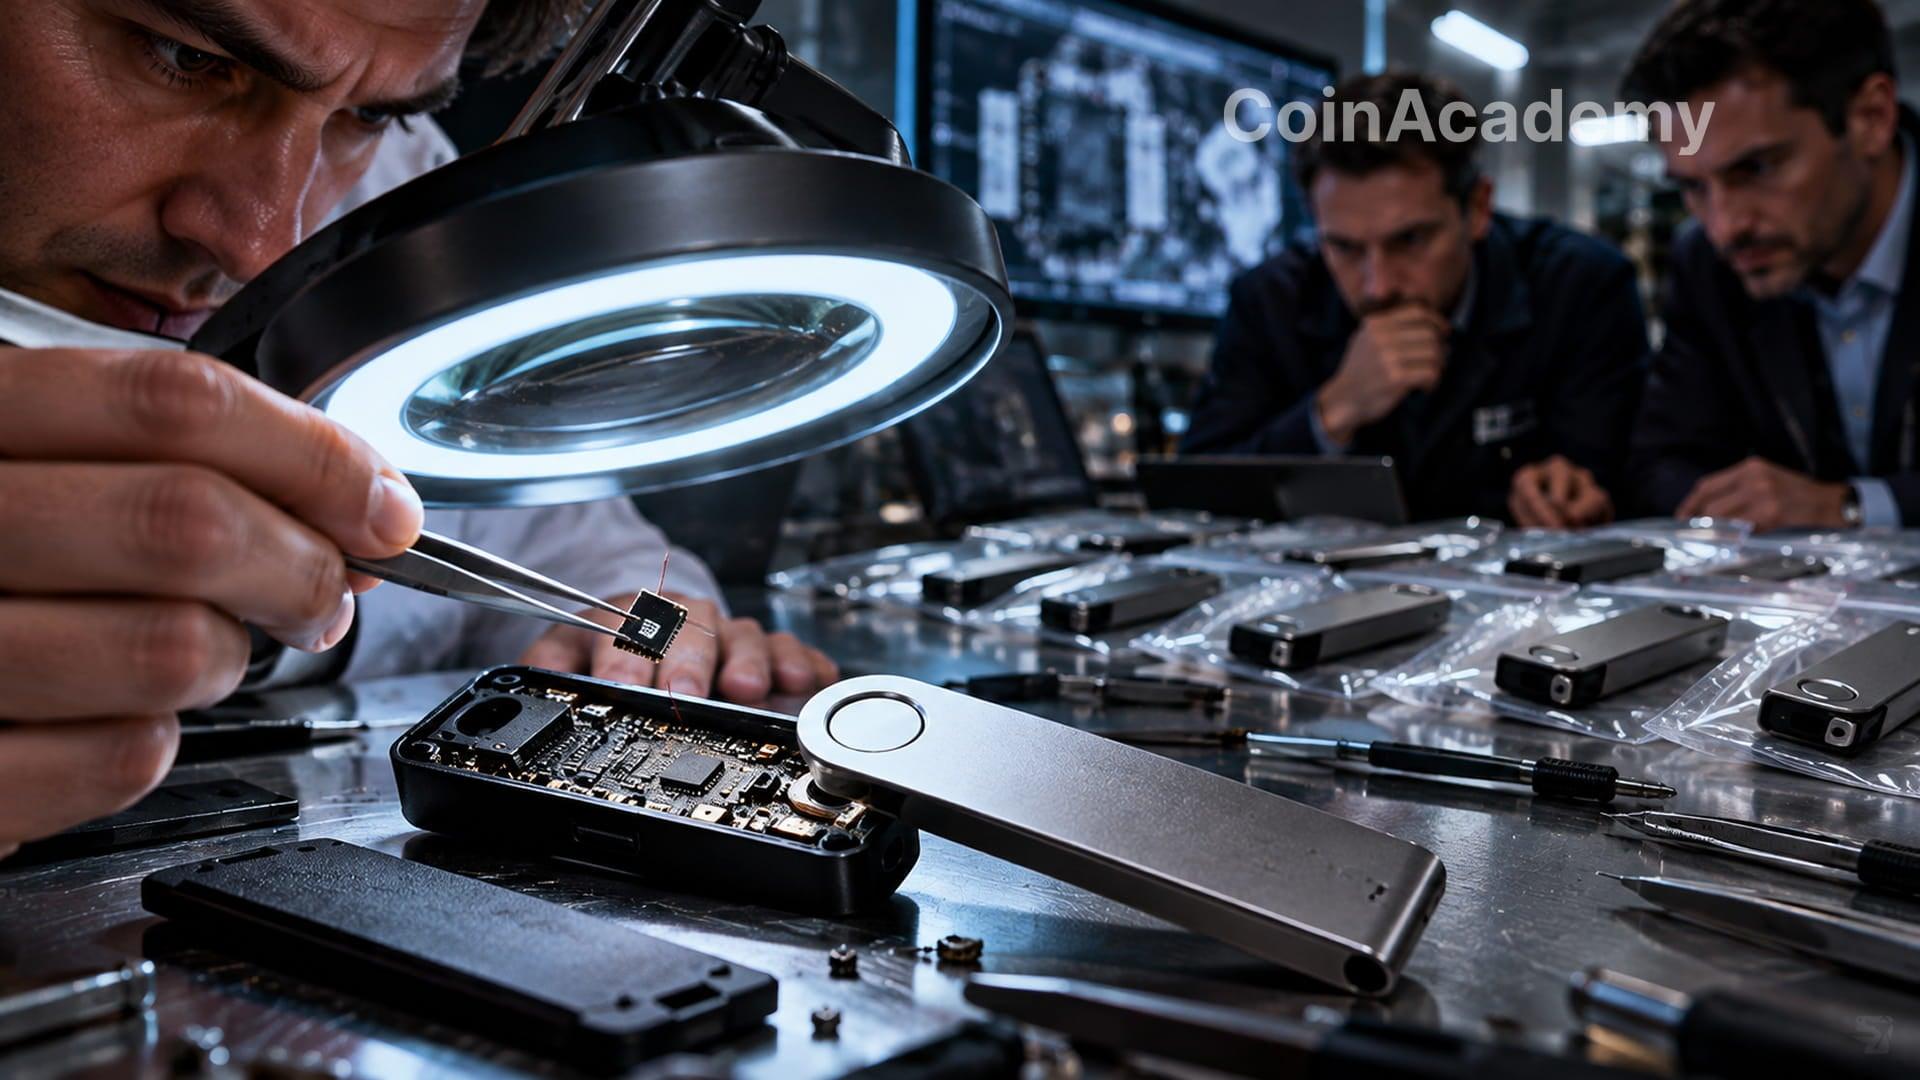
Ledger said the implant sat inside the device enclosure and, when the screen displayed the recovery phrase during setup, its microcontroller recognized and decoded the words before transmitting them over LTE using an eSIM.

Ledger said the recovery phrase is the master key to a crypto wallet and that anyone with it can recreate the wallet elsewhere and move the funds without needing the physical Ledger device or changing any transactions on it.
Onchain researchers estimated losses of up to $93.2 million across more than 300 wallets, and Tether froze $10 million of USDT tied to the theft.
Ledger said it confirmed one affected signer contained an unauthorized implant and that every confirmed loss in the Oct. 9 incident involved a device sold by CryptoBilis.
Resellers cut ties
CryptoBilis said it suspended sales and shipments of all hardware wallet brands in Malaysia, the Philippines and Indonesia, expanding an earlier halt limited to Ledger devices. Trezor said it had received no reports of manipulated Trezor devices sold through CryptoBilis and found no indication that its products were affected, but it removed CryptoBilis from its network of authorized resellers. OneKey reported no related user losses but terminated CryptoBilis’ reseller authorization, suspended onboarding of new resellers, and began reviewing its existing distribution network.
Ledger said it urged users who suspect tampering to contact its support team and file a police report, and it directed concerned customers who bought devices elsewhere to an inspection guide warning that opening a device could damage it. Ledger said it has sold more than 8 million hardware wallets and that it is examining reports beyond the reseller, while X user Johannes posted photos of two Ledger devices he said he bought at MediaMarkt stores with implants.
Europe reports and stakes
Ledger said it had not confirmed the total number of victims or the amount stolen, while onchain researchers estimated losses up to $93.2 million across more than 300 wallets and Specter said losses could exceed $86 million. A European buyer identified as Johannes claimed he bought two Ledger Nano X units at MediaMarkt stores and found “the same modifications,” with extra cables and a hidden LTE module, but Ledger had not confirmed whether the European reports were linked to the CryptoBilis incident. Ledger told customers who bought a device from CryptoBilis not to initialize it, and it told customers who already used one to move assets to a new device with a newly generated recovery phrase.
Ledger also said it has not compromised its software, internal systems, secure element or transaction-signing process, and it described the thefts as a physical supply-chain attack rather than a breach of Ledger’s software or internal systems. Ledger said it was contacting affected users and cooperating with competent authorities, while it also warned that authenticity verification is not enough to rule out the implant if a device has been physically modified.