Crypto · 15 September, 2026 · 2 min read
Uniswap v4 Hook Drains $7.73 Million rsETH From Gnosis Safe Wallet on September 15, 2026
rsETH valued at about $7.7–$7.8 million drained from a Gnosis Safe wallet. An MEV bot front-ran the exploit, transferring a portion of funds.
Whether the outlet covers the rsETH Safe exploit.
2 of 4 outlets skipped it: kelp paused a specific receiving address for 24 hours.
5outlets compared
Same story, two versions
tap a side to read it in full
Blockchain News
“Robinhood token wallet buys $216K at $0.18707 average, now holds $414K with 91.7% unrealized profit”Read the original ↗
Cointelegraph
“The bot captured the rsETH before the original exploiter could take control of the funds”Read the original ↗
Blockchain News (Other) does not report the rsETH Safe-module exploit, focusing on a Robinhood wallet buy instead.
Safe module exploit
An attacker-controlled Uniswap v4 hook converted a leveraged 2,899.99 aEthrsETH position into transferable rsETH, draining a Gnosis Safe wallet at 0x40E93a52F6Af9fCD3b476aeDADD7FeABD9f7AbA8 on the morning of September 15, 2026.
“The victim wallet,0x40E93a52F6Af9fCD3b476aeDADD7FeABD9f7AbA8, is a Gnosis Safe”
Blockaid flagged the incident first and placed confirmed losses at about $7.73 million, while PeckShieldAlert independently pegged the front-run size at roughly $7.81 million.
The victim wallet’s rsETH position was drawn down in a single transaction that burned about 2,899.999999999997756819 aEthrsETH and withdrew the same quantity of rsETH from Aave V3.
Blockaid described the event as “module-authorization abuse on that Safe, not a Safe core / owner-key bug,” tracing execution through a custom Uniswap v4 liquidity provider module and then out of the Safe.
The Yoink MEV searcher executed first in the same Ethereum block, and the primary extraction transaction was included at 04:38:47 UTC in block 25980525.
Yoink front-runs, Kelp freezes
Kelp DAO responded within hours by placing a 24-hour wallet-level pause on the receiving address, while stating that its core contracts and rsETH backing remained unaffected and that standard user operations were continuing as usual.
Cointelegraph reported that Kelp placed the address that received the funds under a 24-hour pause, quoting Kelp: “This is a precautionary, wallet-level measure only,” and adding that “Kelp contracts are safe, rsETH remains fully backed.”C
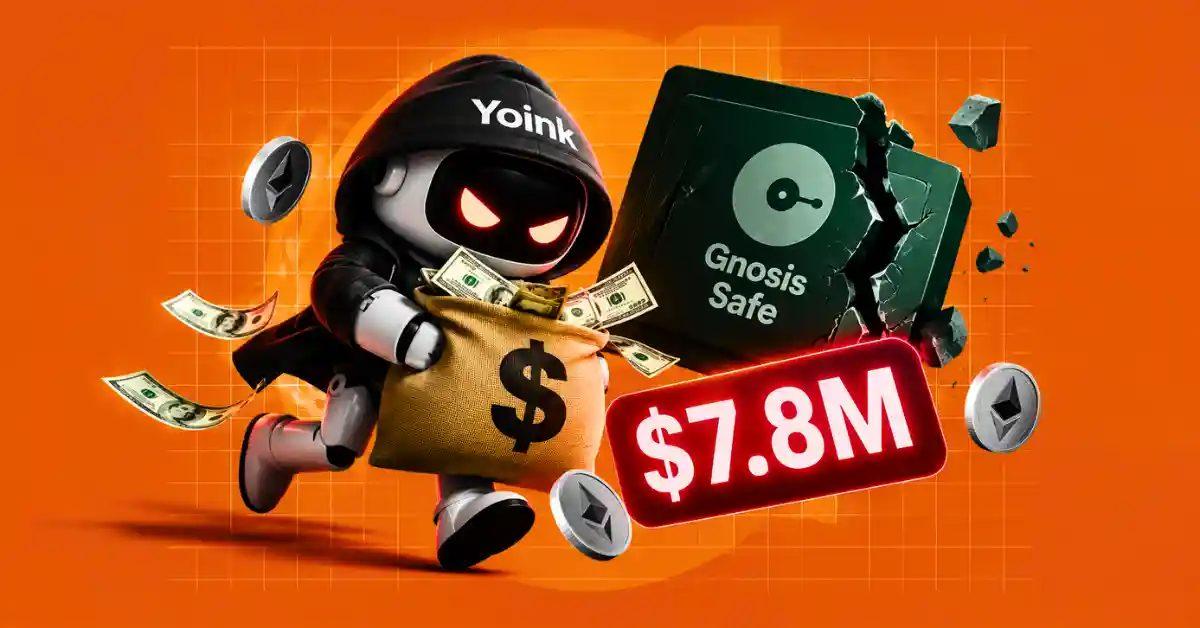
The Crypto Times said a generalized Maximal Extractable Value searcher publicly tagged as “Yoink” executed first in the same Ethereum block, captured the position, and moved the bulk of the tokens to a new receiving address.
Cryptopolitan described the attack as registered on September 15 against a Gnosis Safe wallet user and said the wallet was drained in a single transaction, with the initial attacker and the MEV bot completing the transfers in a single block.
Cryptopolitan further stated that the bot’s destination address now contains only 44 ETH and that the destination address was flagged by Kelp DAO, leading to a freeze of all the deposited rsETH.
What’s at stake next
Kelp DAO’s freeze targeted the receiving address 0xc70f00cd7e461686b04B0E912e309beca8b80ea0, with The Crypto Times saying Kelp posted at 06:03 UTC that it had detected potential suspicious activity on that address.
“At 06:03 UTC, Kelp DAO posted that it haddetectedpotential suspicious activity”
Cryptopolitan said Kelp suspended deposits and withdrawals to prevent the attacker or the bot from moving the funds out of the ecosystem, while also stating that all its vaults were safe so far.
The Crypto Times reported that after the extraction, the bot sent 2,882.37 rsETH, valued at $7,800,883.70, to 0xC70f00CD7E461686b04B0E912E309becA8b80ea0 and swapped the remaining 17.63 rsETH, valued at $47,721.12, through the Uniswap v4 Pool Manager.
Cryptopolitan added that the latest exploit is a rare case of intercepting the funds before being bridged to ETH and laundered through a mixer, and it noted that a vote could revert some of the stolen funds.
The Crypto Times said the Yoink identifier has appeared in prior on-chain reporting on airdrop and claim-contract front-running, while also noting that Etherscan’s public label reflects that history rather than any statement from the operator behind it.